
GUIDE 09 · WEB APPLICATIONS AND APIs
Monitor CVEs and dependencies in your application
Relevant vulnerability alerts need a package, its ecosystem and the exact version used in your release. Supply a supported inventory, review advisory applicability and verify the deployed fix. Scantelio matches advisories to your project’s dependencies instead of sending every CVE to every customer.
Connect dependency monitoringSign-in, ownership verification and consent are required. Authorized scenarios, monitoring and CI require Pro or Business.
On this page
Continuous monitoring versus one scan
New advisory information can appear after a successful release check. Monitoring compares it with the project inventory already supplied. External scanning may identify selected technology signals, but it cannot infer the full package graph or every transitive dependency from a URL.
Provide an inventory tied to a release
Supply exact package versions, ecosystem and provenance. Supported inputs include npm package-lock v2/v3, CycloneDX JSON 1.5/1.6 with package URLs, and supported manual entries. Keep environment, build or commit and collection time. Inventory import parses data; it does not run package installation scripts.
Primary sources: Primary reference 1 · Primary reference 2
Supported ecosystems and formats
The supported ecosystems are npm, PyPI, Maven, Go, crates.io, Packagist, NuGet, RubyGems, Hex and Pub. This does not mean every native manifest in those ecosystems is accepted. Use the documented SBOM format with purl and exact versions; npm also has direct package-lock support.
Distinguish advisory sources and evidence
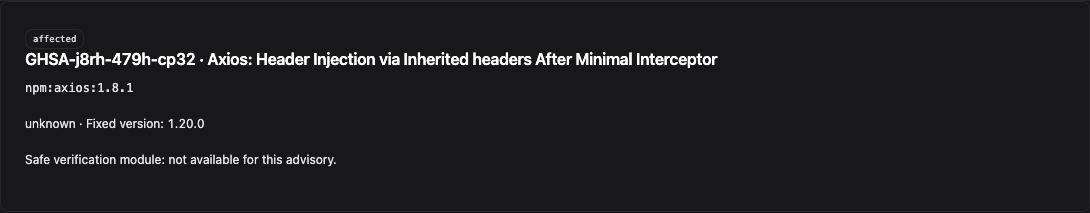
OSV supplies package/version advisory data; NVD provides additional vulnerability context and CISA KEV adds known-exploitation context. A match does not prove exploitation of your application. The reproducible snapshot is GHSA-j8rh-479h-cp32 for axios: 1.8.1 is affected in its stated range; 1.20.0 is the recorded fix boundary as of 2 November 2026.
Primary sources: Primary reference 1 · Primary reference 2
Continue: Next.js security: check APIs, Server Actions and secrets
Connect dependency monitoringPrioritize with application context
Check the affected version, vulnerable feature, exposure, prerequisites and deployed environment. A present package is not proof that the affected feature is reachable. Unknown versions remain uncertain. Do not invent an exploitation conclusion or automatically run an active CVE scenario merely because an inventory matches.
Understand the notification
An alert should identify the project, package, version, advisory and relevant inventory or revision. Notifications are available in the workspace and through configured Telegram conditions, not email. A source outage or stale inventory affects confidence; a general CVE news feed is not project-specific monitoring.
Project: Synthetic fixture
Package: npm / axios 1.8.1
Advisory: GHSA-j8rh-479h-cp32
Inventory: guide-before
Next step: update, deploy and submit the new inventory.
Primary sources: Primary reference 1 · Primary reference 2
Continue: Vibe coding security: check your application before launch
Verify the updated release
Update the dependency, build and deploy the application, then submit an inventory for that revision. The example runs the actual parser and matcher against two synthetic lockfiles: guide-before matches this advisory; guide-after does not. It does not claim that version 1.20.0 has no other advisories or that a customer deployment was changed.
| Fixture revision | Package | Version | This advisory |
|---|---|---|---|
| guide-before | axios | 1.8.1 | affected |
| guide-after | axios | 1.20.0 | not_affected |
Keep the evidence current
Refresh inventory after every relevant deployment and review source freshness. Withdrawn advisories and changed ranges can change the result. A manual snapshot does not prove current production composition. Keep the original match, the fixed build identifier and the new inventory to support an auditable resolution.
Reproducible examples and downloads
All example data is synthetic. Downloads contain no active keys or customer records. Run examples only in your own isolated test environment.
Example verification record: versions, actions and observations
Questions and answers
Will I receive every new CVE?
No. Alerts are based on the relevant dependencies and affected versions supplied for your project.
Can Scantelio discover all packages from a URL?
No. Provide a supported dependency inventory with exact versions.
Are only npm projects supported?
Ten ecosystems are supported through the documented formats; npm additionally supports package-lock import.
Does an advisory match prove exploitation?
No. Applicability and actual exploitation are different questions.
Is editing package.json enough?
No. Verify the installed and deployed build and submit its updated inventory.
Can an advisory change later?
Yes. Ranges, fix information or withdrawal status may change, so monitoring must refresh source data.
Editorial team and sources
Scantelio editorial team: methodology and limitations. Example verified: 2026-11-02.
Apply the check to your own project
Connect dependency monitoringChoose your project after signing in. No scan runs without verification and consent.