
GUIDE 07 · WEB APPLICATIONS AND APIs
Exposed .env, .git or API keys: contain the leak and verify the fix
If a working credential has been exposed, revoke or rotate it first and check its use. Removing a file or deleting a repository line does not invalidate a copied key. Then close the publication path, redeploy and verify that both the old credential and the exposed resource no longer provide access.
On this page
Act immediately
Identify the exposed credential and the services it can access. Revoke it or rotate it through the provider, update authorized consumers and confirm that the old value no longer works. Preserve a limited incident record without redistributing the secret. Avoid waiting for a scan before containment.
Confirm what was exposed
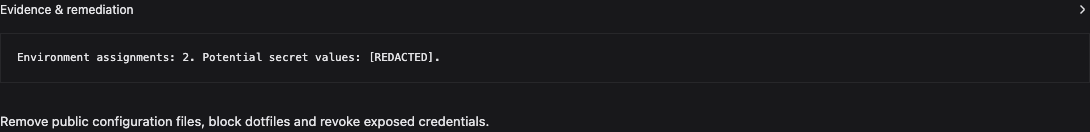
Inspect the exact authorized path and response structure. A 200 response containing a SPA shell does not prove a configuration leak. Our local fixture compares configuration content with a SPA fallback and a 404. The Scantelio rule checks structural signals and omits secret values from its evidence.
Primary sources: Primary reference 1 · Primary reference 2
Continue: Check your own website for vulnerabilities by URL
Check the leak fixWhy deleting the line is insufficient
Copies can remain in repository history, cached responses, build artifacts, logs or other systems. Closing the visible file path stops one distribution channel; it does not remove previously copied credentials. Revocation and rotation are separate actions from cleanup.
Investigate possible use
Review the provider’s audit and access logs, the credential’s permissions and its exposure window. Determine whether unauthorized operations occurred and follow your incident process. An external scanner finding does not independently establish that an attacker used the key or quantify the impact.
python3 access-fixture.py
curl -H "X-Fixture-User: a" "http://127.0.0.1:8769/documents/doc-b?mode=vulnerable"
curl -H "X-Fixture-User: a" "http://127.0.0.1:8769/documents/doc-b?mode=fixed"
Primary sources: Primary reference 1 · Primary reference 2
Continue: Next.js security: check APIs, Server Actions and secrets
Trace the publication path
Look at static build directories, deployment packaging, web-server rules, source maps, backups and debug handlers. Distinguish a public client configuration value from a privileged secret. Check whether generated code copied a server-only value into a client bundle or response.
Fix the underlying cause
Keep configuration outside public web roots, restrict served artifacts and remove unintended debug or repository exposure. Store active secrets in the appropriate deployment secret mechanism. Review the build output and routing behavior; merely changing a filename is not a durable fix.
Primary sources: Primary reference 1 · Primary reference 2
Verify containment and the release
Confirm that the old key is rejected, the original path no longer exposes configuration and legitimate application behavior still works. Use a targeted retest for the observed finding. A login page, WAF block or timeout can make the scanner result inconclusive rather than proving a fix.
Prevent recurrence
Add artifact review and supported external checks to the release process. Use source-host secret detection where available as a separate safeguard, maintain a rotation procedure and keep least-privilege credentials. Scantelio does not claim to purge every historical copy or automatically repair repositories.
Reproducible examples and downloads
All example data is synthetic. Downloads contain no active keys or customer records. Run examples only in your own isolated test environment.
Example verification record: versions, actions and observations
Questions and answers
Should I scan before rotating the key?
Contain an actual credential exposure immediately; scanning is not a prerequisite for revocation.
Does deleting the repository line revoke a token?
No. Revoke or rotate it with its issuing service.
Is every public configuration value a secret?
No. Classify the value and its permissions; public-client configuration is different from a privileged credential.
Does HTTP 200 prove a leak?
No. Inspect structural evidence and exclude SPA or login-page fallbacks.
Will the report include my secret?
Evidence should omit or redact sensitive values. Do not upload real credentials into example material.
Does a clean retest prove there was no misuse?
No. Retesting checks current behavior; incident investigation needs the relevant service logs.
Editorial team and sources
Scantelio editorial team: methodology and limitations. Example verified: 2026-11-02.
Apply the check to your own project
Check the leak fixChoose your project after signing in. No scan runs without verification and consent.