
GUIDE 02 · WEB APPLICATIONS AND APIs
Check your own website for vulnerabilities by URL
Add your website to Scantelio, verify ownership and approve the scan. External checks inspect supported HTTPS/TLS settings, HTTP responses and exposed configuration. Private permissions and the complete library inventory need additional data; one URL does not provide full application coverage.
Check your websiteSign-in, ownership verification and consent are required. Start with the limited Free external profile.
On this page
Start a check of your website
Open your workspace, create or select the project and add its exact website or API address. Verify the allowed host and path prefix using the supported proof method, then grant scan consent. Select an environment and a profile; opening this guide does not start a scan.
What external checks cover
The supported external profile checks TLS, relevant security headers, CORS responses, configuration exposure and debug output. The reviewed Nuclei pack contains nine short-profile rules and forty full-profile rules. Declaring the component stack avoids unrelated specialized checks; a rule count is not a guarantee of complete coverage.
Primary sources: Primary reference 1 · Primary reference 2
Continue: Vibe coding security: check your application before launch
How a scan proceeds
The system checks scope and consent, reserves the applicable quota and queues the run. Actual execution begins when a worker takes it. The report distinguishes completed checks, findings, skipped checks and uncertainty. Waiting-time estimates can change with capacity and the duration of earlier work.
What a useful report contains
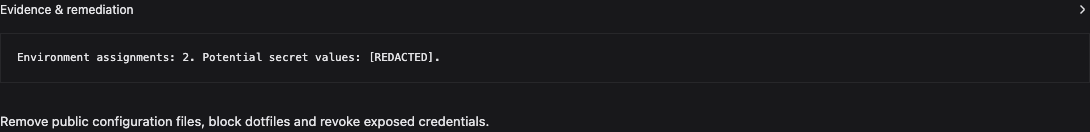
Look for the affected operation, observed evidence, confidence, remediation and coverage limitations. A confirmed finding and a suspicion are different outcomes. The example below uses a local synthetic configuration response and the actual Scantelio rule; it is not a customer scan or a claim about an arbitrary website.
python3 access-fixture.py
curl -H "X-Fixture-User: a" "http://127.0.0.1:8769/documents/doc-b?mode=vulnerable"
curl -H "X-Fixture-User: a" "http://127.0.0.1:8769/documents/doc-b?mode=fixed"
Primary sources: Primary reference 1 · Primary reference 2
Continue: Prepare an automated API security assessment
Check your websiteWhy HTTP 200 does not prove a leaked file
Many single-page applications return the same HTML for every unknown path. A scanner must inspect structure and use controls instead of equating success status with a leak. Our example compares configuration content, a SPA fallback and an unavailable file. Secret-like values are not included in exported evidence.
| Fixture response | Observation | Conclusion |
|---|---|---|
| 200, configuration content | Structural configuration signals | Finding; sensitive values omitted |
| 200, SPA HTML | No configuration structure | No confirmed leak |
| 404 | Resource unavailable | This path passed; not proof of complete security |
Interpret headers, CORS and certificates in context
An absent HTML protection header is different from a vulnerable API permission check. Public CORS wildcard access alone is not an authorization bypass. Cookie-credential CORS observations need further confirmation. A certificate check observes the configured endpoint; it does not inspect every deployment or business operation.
Primary sources: Primary reference 1 · Primary reference 2
Continue: Exposed .env, .git or API keys: contain the leak and verify the fix
Free and extended checks
Free provides the currently configured limited short checks. Pro and Business enable broader workflows within their budgets; their supported detection quality is the same. Prices, limits and feature switches below come from the live catalog. Disabled billing does not mean a paid subscription was purchased.
Act on the result
Verify the affected configuration, apply a reviewed fix and repeat the same scenario. Keep an authorized control so a broken or unavailable application is not marked fixed. Add API accounts or an inventory when the initial scan exposes a coverage gap, then use recurring checks where available.
Reproducible examples and downloads
All example data is synthetic. Downloads contain no active keys or customer records. Run examples only in your own isolated test environment.
Example verification record: versions, actions and observations
Questions and answers
Is registration required?
Yes, to connect a project, prove ownership and approve a scan. Reading these guides needs no account.
Can this check private API data?
Only configured authorized scenarios can assess private objects and roles; a public URL alone is insufficient.
Can I check someone else’s website?
Only with explicit permission and the required ownership or scope verification.
Does no finding mean complete security?
No. It describes completed scenarios, not every possible weakness.
What if the site returns a login page or WAF challenge?
Treat it as a limitation of coverage, not evidence that the protected resource is safe.
Are all plans shown here?
Yes. The table loads all current plans, prices and limits from the application catalog.
Editorial team and sources
Scantelio editorial team: methodology and limitations. Example verified: 2026-11-02.
Apply the check to your own project
Check your websiteChoose your project after signing in. No scan runs without verification and consent.